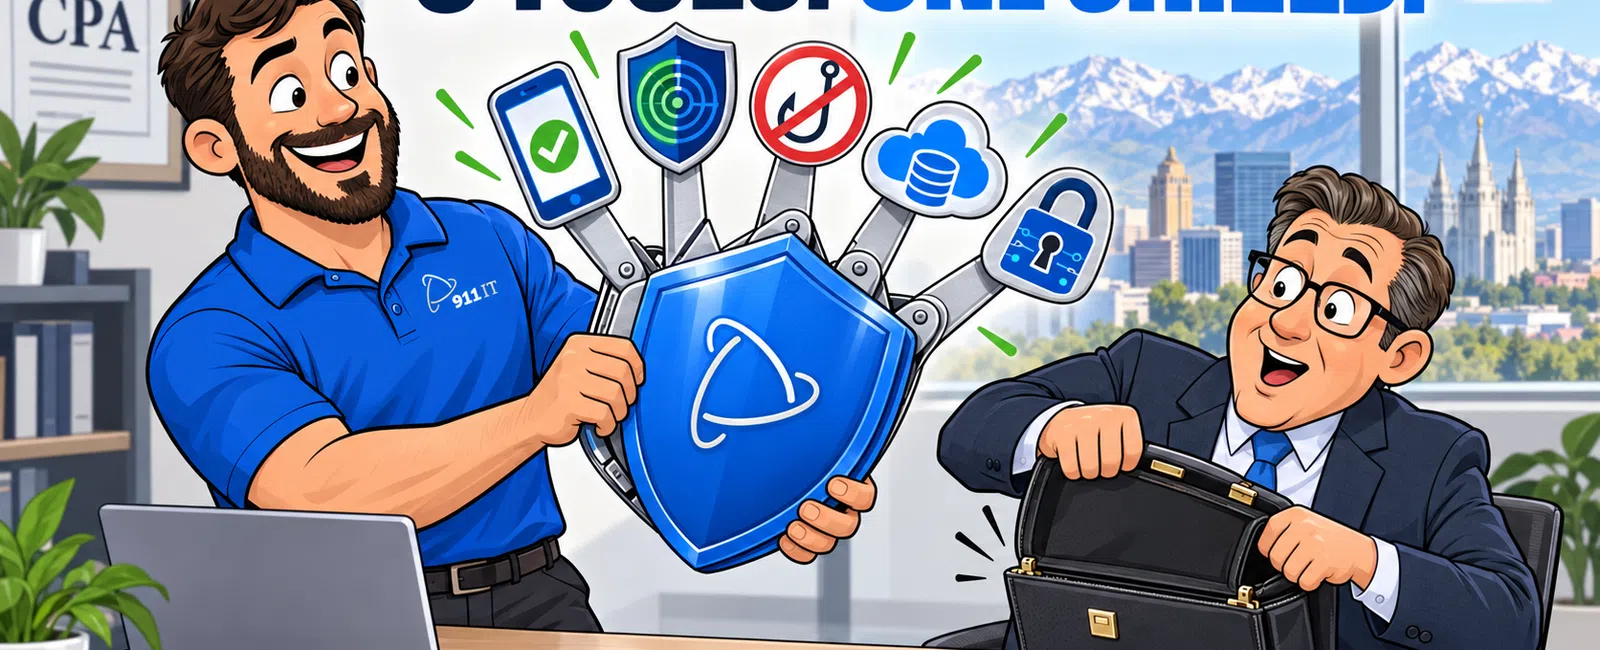
The top five cybersecurity tools for CPA firms in Salt Lake City are endpoint detection and response (EDR) platforms, multi-factor authentication (MFA) systems, encrypted email and file-sharing solutions, network firewalls with intrusion prevention, and security awareness training platforms. These five tools work together to protect sensitive taxpayer data, prevent unauthorized access to engagement files, and maintain compliance with IRS Publication 4557 safeguarding requirements during busy season and year-round.
Why Do CPA Firms Need Specialized Cybersecurity Tools?
CPA firms handle extraordinarily sensitive data - Social Security numbers, bank account details, tax returns, and financial statements - making them prime targets for cybercriminals. A single breach can expose hundreds or thousands of clients' personal information, triggering Utah's data breach notification laws and destroying the trust that took years to build.
The IRS explicitly requires tax preparers to have a written information security plan under Publication 4557. This isn't optional guidance; it's a regulatory expectation that includes specific technical safeguards. Firms without proper tools face not only breach risk but potential liability for failing to meet professional standards.
Tax season creates unique pressure points. When your team is working 60-hour weeks processing 1040s and 1120s, they're more likely to click a phishing link or skip security steps. Your cybersecurity tools must work automatically in the background, protecting your firm even when staff are exhausted and distracted.
Salt Lake City's growing financial services sector means more CPA firms competing for the same clients. Demonstrating robust security isn't just about compliance - it's a competitive advantage when prospects ask how you'll protect their data.
What Is Endpoint Detection and Response and Why Is It Essential?
Endpoint detection and response (EDR) platforms monitor every workstation and laptop in your firm for suspicious behavior. Unlike traditional antivirus that only catches known threats, EDR uses behavioral analysis to identify ransomware, zero-day exploits, and advanced persistent threats in real time.
When a staff member opens a malicious attachment, EDR can isolate that machine from your network within seconds, preventing the infection from spreading to your file server where years of client workpapers reside. This containment capability is critical for firms that can't afford downtime during March and April.
Modern EDR solutions also provide forensic capabilities. If you do experience an incident, you can trace exactly what happened - which files were accessed, what data was exfiltrated, which clients need to be notified. This audit trail is invaluable for both incident response and demonstrating due diligence to regulators.
Scott, an engineering firm client, noted that 911 IT's cybersecurity protection on computer systems connected to their network allowed his team to focus on core business while safely managing cloud-based services. The same principle applies to CPA firms: your technology should protect you without requiring constant attention from partners who need to focus on client service.
EDR is non-negotiable for any firm handling taxpayer data.
How Does Multi-Factor Authentication Protect Client Portals and Remote Access?
Multi-factor authentication (MFA) requires users to provide two or more verification factors to access systems - typically something they know (password) plus something they have (phone app code) or something they are (fingerprint). This single control prevents the vast majority of credential-based attacks.
CPA firms increasingly use remote desktop solutions so staff can work from home or access the office network while meeting clients. Without MFA, a compromised password - leaked in a data breach at an unrelated service - gives attackers full access to your practice management software, tax preparation systems, and client files.
Client portals where you share completed returns and financial statements are another critical access point. If a client uses a weak password and their email is compromised, attackers can log into your portal and access sensitive documents. MFA adds a layer that stops this attack vector cold.
Utah's data breach notification law requires firms to notify affected individuals when unencrypted personal information is accessed by unauthorized persons. MFA significantly reduces the likelihood you'll ever need to make those notifications, protecting both your clients and your reputation.
Implementation is straightforward with modern identity platforms that integrate with Microsoft 365, QuickBooks, and tax software. The minor inconvenience of a six-digit code is trivial compared to the protection it provides.
What Makes Encrypted Email and File Sharing Critical for Tax Documents?
Standard email transmits messages in plain text, readable by anyone who intercepts them in transit. When you email a client's tax return or financial statements, you're potentially exposing that data to compromise at multiple points between your server and theirs.
Encrypted email solutions wrap messages in strong encryption, ensuring only the intended recipient can decrypt and read them. For CPA firms, this is essential for transmitting engagement letters, representation letters, and completed returns that contain Social Security numbers and financial details.
Secure file-sharing platforms provide an alternative to email attachments. Instead of sending a 10MB PDF of a compiled financial statement, you upload it to an encrypted portal and send the client a secure link. These platforms typically include access controls (who can view, download, or share), expiration dates, and audit logs showing exactly when files were accessed.
The IRS specifically addresses secure transmission in Publication 4557, noting that practitioners should use encryption for emails containing sensitive taxpayer information. This isn't just best practice - it's part of your professional obligation to safeguard client data.
Many CPA firms in Salt Lake City have adopted these tools as table stakes. If you're still emailing unencrypted tax returns, you're falling behind both regulatory expectations and client expectations for modern, secure service.
How Do Network Firewalls with Intrusion Prevention Stop External Attacks?
A network firewall sits at the perimeter of your firm's network, controlling what traffic can enter and exit. Modern firewalls include intrusion prevention systems (IPS) that actively block known attack patterns, malicious IP addresses, and suspicious connection attempts.
For CPA firms, the firewall is your first line of defense against external threats. It prevents unauthorized access attempts to your file servers, blocks connections to known command-and-control servers used by malware, and can detect and stop data exfiltration attempts when attackers try to steal your client database.
Next-generation firewalls add application awareness, allowing you to control not just which ports are open but which specific applications can communicate. You might allow Microsoft Teams for video calls with clients but block peer-to-peer file-sharing applications that create security risks.
Garry, an engineering firm client, experienced no major outages while working with 911 IT, with any minor issues resolved quickly and effectively. That reliability stems partly from properly configured network security that prevents problems before they impact operations. The same proactive approach protects CPA firms from the attacks that cause downtime during your busiest weeks.
Firewall management requires ongoing attention - firmware updates, rule reviews, log analysis - which is why many Salt Lake City CPA firms partner with managed IT providers who monitor these systems 24/7 rather than expecting a part-time bookkeeper to handle network security.
Why Is Security Awareness Training Your Most Important Tool?
Technology alone cannot stop every threat. Your staff remain the most common entry point for cyberattacks through phishing emails, social engineering phone calls, and simple mistakes like leaving laptops in cars or sharing passwords.
Security awareness training platforms deliver regular, bite-sized lessons on recognizing phishing attempts, handling sensitive data, using strong passwords, and reporting suspicious activity. The best platforms include simulated phishing campaigns that test whether staff actually apply what they've learned.
During tax season, when your team is processing hundreds of returns under deadline pressure, they're most vulnerable to clicking a malicious link in an email that appears to come from a client or the IRS. Regular training builds muscle memory that helps staff pause and verify before clicking, even when they're exhausted.
The IRS has repeatedly warned about phishing campaigns targeting tax professionals, including sophisticated attacks that spoof IRS e-services or tax software vendors. Your staff need to recognize these attempts and know exactly what to do when they receive one.
Sam, a fundraising client, noted that after a security audit with 911 IT, he was able to identify and fix security issues, sleeping better knowing his systems and data were safe. He valued the information provided at 10X what the audit cost. That same peace of mind comes from knowing your staff are trained to be your first line of defense, not your weakest link.
Firms that combine all five tools - EDR, MFA, encrypted communication, network firewalls, and staff training - reduce their breach risk by over 90% compared to firms relying on basic antivirus alone.
How Do These Tools Work Together as a Layered Defense?
Cybersecurity professionals call this approach "defense in depth" - multiple overlapping layers so that if one control fails, others still protect you. No single tool is perfect, but together they create a system where attackers must bypass multiple defenses to succeed.
Consider a realistic attack scenario:
- A staff member receives a phishing email that bypasses your spam filter
- Security awareness training should help them recognize and delete it, but assume they click the malicious link
- The EDR platform detects the malware attempting to execute and blocks it
- If somehow the malware runs, the network firewall prevents it from connecting to its command-and-control server
- If the attacker tries to move laterally to access your file server, MFA blocks them from logging in with stolen credentials
- If they attempt to exfiltrate data, encrypted file systems make the stolen data useless
This layered approach is particularly important for CPA firms because you face sophisticated, targeted attacks. Cybercriminals know tax season means you're handling massive volumes of sensitive data and are less likely to notice anomalies. They specifically target accounting firms for this reason.
Implementation doesn't require a massive IT department. Many Salt Lake City CPA firms work with specialized IT providers who understand accounting firm workflows and can deploy and manage these tools without disrupting operations or requiring partners to become security experts.
The investment is modest compared to the cost of a breach - both the direct costs of incident response, notification, and potential lawsuits, and the indirect costs of reputation damage and lost clients who no longer trust you with their financial information.
What Should Salt Lake City CPA Firms Look for in a Cybersecurity Partner?
Not all IT providers understand the specific needs and compliance requirements of CPA firms. You need a partner who knows IRS Publication 4557, understands the pressure of tax season, and has experience protecting engagement files and taxpayer data.
Look for providers who offer comprehensive cybersecurity services including all five essential tools discussed above, not just basic antivirus and backup. Ask about their monitoring capabilities - can they detect and respond to threats 24/7, or will an attack that starts Friday evening run unchecked until Monday morning?
Response time matters enormously during busy season. If your tax software goes down on April 10th, you need help immediately, not a ticket that sits in a queue for 24 hours. Ask about guaranteed response times and whether you'll work with the same technicians who understand your systems or get a different person each time.
Local providers often offer advantages for CPA firms. They understand Utah's regulatory environment, can provide on-site support when needed, and treat you as a valued client rather than one account among thousands. At large national MSPs, a small CPA firm is a ticket number; at a regional provider like 911 IT, you're a known partner whose business matters.
911 IT serves CPA firms and financial services companies throughout Salt Lake City and Utah with proactive managed IT services that include all five essential cybersecurity tools. With 24/7 monitoring and helpdesk support, flat-rate transparent pricing, and a 100% satisfaction guarantee, 911 IT provides the security infrastructure that lets you focus on serving clients rather than worrying about technology. The firm's Process-Driven Excellence and proven track record with professional services firms - evidenced by their 2024 MSP Titans award and Best of Salt Lake recognition - make them the right-sized partner for CPA firms who need enterprise-grade security without enterprise-level complexity.
Frequently Asked Questions
What is the most important cybersecurity tool for a small CPA firm?
Multi-factor authentication is the single most impactful tool for small CPA firms because it prevents the majority of credential-based attacks with minimal cost and complexity. Combined with security awareness training, MFA stops most common threats that target accounting practices. However, comprehensive protection requires all five tools working together as a layered defense system.
How much do cybersecurity tools cost for a CPA firm?
Industry-average cybersecurity services including EDR, MFA, encrypted communication, firewall management, and security training typically cost $25 - $75 per user per month as an add-on to managed IT services. For a five-person CPA firm, expect $125 - $375 monthly for comprehensive protection. This investment is modest compared to the average cost of a data breach, which exceeds $50,000 for small firms.
Do I need different tools during tax season versus the rest of the year?
No, you need the same tools year-round, but monitoring and support become more critical during busy season when your team is working long hours and more vulnerable to mistakes. Your cybersecurity partner should provide 24/7 monitoring and rapid response during tax season when downtime is most costly. The tools themselves remain constant, but human vigilance and professional support intensity should increase.
Can I implement these tools myself or do I need an IT provider?
While technically possible to implement these tools yourself, most CPA firms lack the time and expertise to properly configure, monitor, and maintain them. Effective cybersecurity requires ongoing attention - firmware updates, log analysis, threat response - that distracts from client service. Most Salt Lake City CPA firms find partnering with a specialized IT provider more cost-effective than hiring internal IT staff or burdening partners with security responsibilities.
How do I know if my current IT provider is giving me adequate protection?
Ask your provider specifically whether you have EDR (not just antivirus), MFA on all remote access and admin accounts, encrypted email for tax documents, a next-generation firewall with IPS, and regular security awareness training with simulated phishing. Request evidence of 24/7 monitoring and recent security reports. If they can't clearly demonstrate all five layers, your protection likely has gaps that put client data at risk.