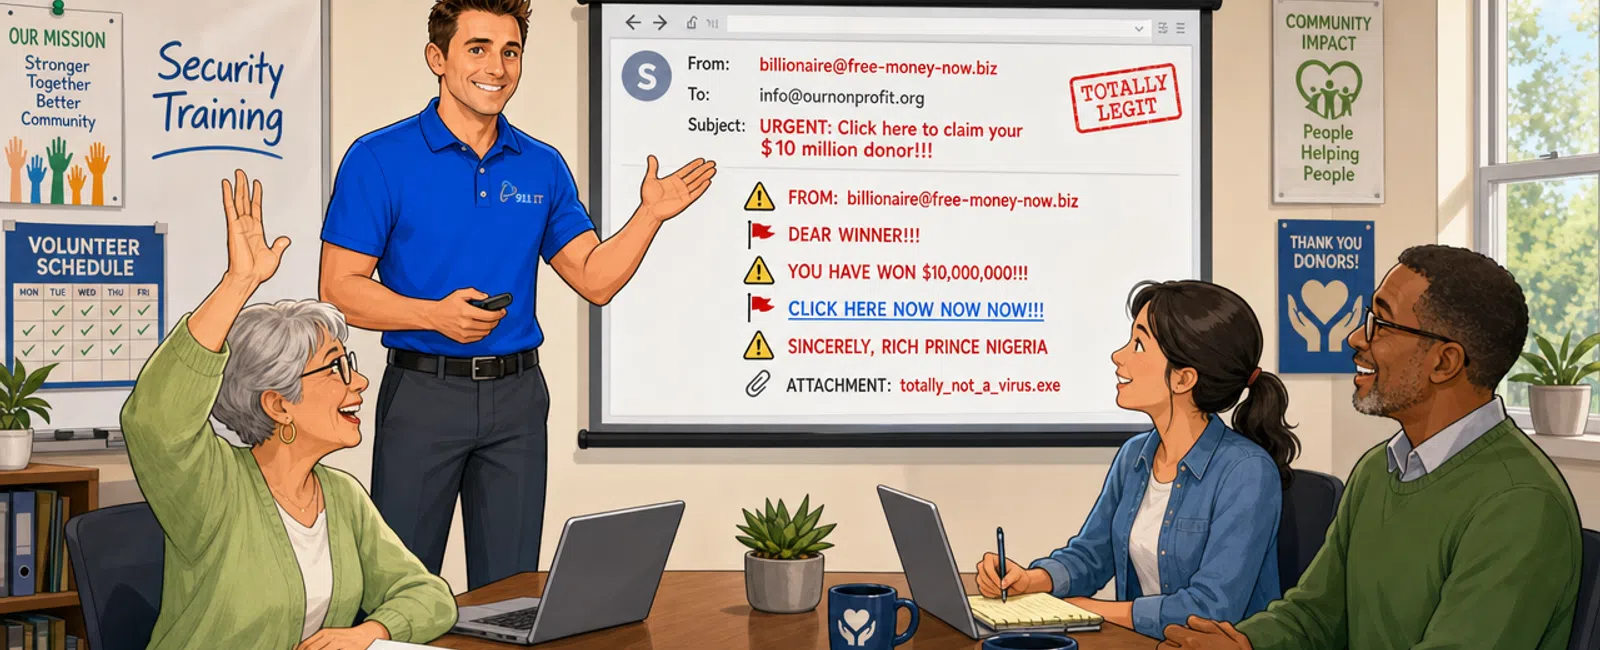
911 IT provides hands-on cybersecurity awareness training specifically designed for non-technical staff, covering phishing recognition, password management, safe data handling, and incident reporting. Training includes simulated phishing campaigns, quarterly refresher sessions, and 24-7 helpdesk support to answer security questions as they arise. Programs reduce successful phishing incidents by over 70% within six months, with customized modules addressing workflows from volunteer coordination to donor database protection.
Why Do Nonprofits Need Security Training for Non-Technical Staff?
Nonprofits face unique cybersecurity risks because they handle sensitive donor information, beneficiary records, and grant compliance data while operating on limited budgets. Staff members who aren't tech-savvy represent the largest vulnerability: 82% of data breaches involve a human element.
In Salt Lake City's nonprofit sector, organizations often rely on volunteers, part-time staff, and mission-focused employees who may lack formal IT training. These team members open donor databases, process online donations, and communicate with beneficiaries - all activities that create security exposure if not done correctly.
The consequences of a breach extend beyond financial loss. A ransomware attack that locks donor records can halt fundraising operations. A phishing incident that compromises beneficiary data can damage community trust and violate grant compliance requirements under federal and Utah state regulations.
Kenton, who leads a local nonprofit, described his experience after switching to 911 IT: "After switching to 911 IT from a provider that wasn't meeting our needs, I was immediately impressed. I've needed support a few times now, and each experience showed me everything I needed to know - they were fast, helpful, and clearly committed to taking care of their clients."
Effective security training transforms your team from a vulnerability into a defense layer, catching threats before they escalate into incidents.
What Topics Does Security Awareness Training Cover?
Comprehensive training for non-technical staff addresses the specific scenarios employees encounter daily, not abstract concepts. The curriculum focuses on practical, immediately applicable skills.
Phishing and email security training teaches staff to recognize suspicious messages, verify sender authenticity, and report potential threats. Simulated phishing campaigns provide safe practice opportunities, with results tracked to identify teams needing additional support.
Password hygiene and multi-factor authentication modules explain why "DonorDatabase2024" isn't secure and demonstrate how to create strong, unique passwords. Training covers password manager tools and the importance of enabling two-factor authentication on donor management systems and email accounts.
Safe data handling practices address how to store donor information, when encryption is required, and proper procedures for sharing sensitive files. For Salt Lake City nonprofits handling Utah charitable solicitation data, this includes compliance with state privacy requirements.
Physical security awareness covers locking workstations when stepping away, securing devices during community events, and protecting printed donor reports. Many breaches occur through unlocked computers in shared office spaces.
Incident reporting procedures ensure staff know exactly whom to contact and what steps to take when something seems wrong. Fast reporting can mean the difference between containing a threat and experiencing a full breach.
Training materials use nonprofit-specific examples - donor database scenarios, volunteer coordination platform access, and grant reporting systems - so concepts feel relevant rather than generic.
How Is Training Delivered to Accommodate Different Learning Styles?
Effective security training recognizes that nonprofit staff have varying technical backgrounds, learning preferences, and availability constraints. A one-size-fits-all approach leaves gaps.
Interactive online modules allow staff to complete training at their own pace, with short 10-15 minute segments that fit around program delivery responsibilities. Content includes videos, quizzes, and scenario-based exercises that reinforce concepts.
Live group sessions provide opportunities for questions and discussion, particularly valuable for teams that work closely together. These sessions can be conducted on-site or via video conference to accommodate remote volunteers and satellite office staff.
Role-specific training tracks address the distinct needs of different positions. Executive directors receive training on board reporting and fiduciary responsibility for data protection. Development staff get specialized modules on donation platform security. Program coordinators learn about beneficiary data handling.
Hands-on practice exercises let staff apply concepts in controlled environments. This might include practicing how to verify a suspicious donation email or demonstrating proper procedures for accessing donor records from a home office.
Quick-reference materials provide desk-side reminders and decision trees. A laminated card explaining "Is this email safe to open?" helps staff make real-time decisions without memorizing complex rules.
Rebekah from a Salt Lake City nonprofit noted: "Working with 911 IT has been a fantastic experience. Their IT support team is not only highly knowledgeable but also personable and fun to interact with - making even frustrating tech issues feel less stressful."
The goal is building confidence, not creating anxiety about technology.
How Often Should Security Training Be Refreshed?
Cybersecurity threats evolve constantly, and human memory fades without reinforcement. One-time training provides temporary awareness that deteriorates within months.
Initial comprehensive training establishes the foundation when staff join the organization or when a security program launches. This typically requires 60-90 minutes of focused attention covering all core topics.
Quarterly refresher sessions reinforce key concepts and introduce new threat patterns. These shorter 15-20 minute updates keep security top-of-mind without overwhelming busy nonprofit staff. Content focuses on recent phishing trends or newly discovered vulnerabilities.
Monthly simulated phishing tests provide ongoing practice in a low-stakes environment. Staff who click simulated phishing links receive immediate, non-punitive coaching. Organizations track improvement over time to measure program effectiveness.
Just-in-time micro-training delivers brief reminders when relevant. Before year-end fundraising campaigns, staff receive a quick refresher on donation email verification. Before tax season, a reminder about W-9 phishing scams goes out.
Annual comprehensive reviews ensure all staff remain current as threats evolve and as Utah regulatory requirements change. This also serves as onboarding for new team members who joined mid-year.
Event-triggered training occurs after security incidents - either at your organization or widely publicized breaches affecting similar nonprofits. These sessions explain what happened, why, and how your team can avoid similar situations.
Consistent reinforcement transforms security awareness from a checkbox exercise into organizational culture.
What Support Is Available When Staff Have Security Questions?
Training provides knowledge, but real-world situations generate questions that need immediate answers. Non-technical staff need accessible support channels that don't make them feel foolish for asking.
911 IT provides 24-7 helpdesk support staffed by live technicians who understand nonprofit operations. When a development coordinator receives a suspicious donation notification at 7 PM during a fundraising event, they can call immediately for guidance rather than guessing or waiting until morning.
The one-hour-or-less emergency response time ensures security questions get answered before small concerns become major incidents. If a staff member accidentally clicks a suspicious link, rapid response can contain the threat before it spreads through your network.
Support technicians are trained to explain security concepts in plain language, not technical jargon. They understand that asking "Is this email safe?" represents good security practice, not incompetence. This approach encourages staff to seek help rather than making risky decisions alone.
Melia from a financial services firm described this teaching approach: "What I love most about working with 911 IT is how easy it is to reach out with any issue - big or small. The staff don't just fix problems; they take the time to teach us how to handle simple things ourselves moving forward."
Documentation and knowledge base resources provide self-service options for common questions. Staff can quickly look up "how to verify a wire transfer request" or "steps to report a lost device" without waiting for a callback.
Regular check-ins with nonprofit leadership ensure training programs address emerging questions and adjust to changing organizational needs. As your nonprofit adopts new fundraising platforms or grant management tools, training evolves accordingly.
911 IT's security training programs have helped nonprofit clients reduce successful phishing incidents by over 70% within six months of implementation.
How Do Salt Lake City Nonprofits Choose the Right Security Training Partner?
Selecting a security training provider requires evaluating both technical expertise and understanding of nonprofit operations. Not all IT firms grasp the unique constraints and priorities of mission-driven organizations.
Consider providers with documented experience serving Salt Lake City nonprofits who understand Utah charitable solicitation requirements and the local philanthropic landscape. Generic training designed for corporate environments often misses nonprofit-specific scenarios around donor data, volunteer access, and grant compliance.
Evaluate training delivery flexibility. Nonprofits need programs that accommodate part-time staff, volunteers with limited availability, and teams spread across multiple locations. Rigid training schedules that assume 9-to-5 office presence won't work.
Look for ongoing support infrastructure, not just one-time training events. The provider should offer accessible helpdesk support when staff encounter real security questions, plus regular program updates as threats evolve.
Verify the provider's commitment to education over intimidation. Security training should empower staff to make good decisions, not create fear that paralyzes normal operations. Ask how the provider handles staff who make mistakes during simulated phishing tests.
In Salt Lake City's managed IT landscape, several providers serve nonprofits:
- Executech offers enterprise-focused IT services with security training components
- Wasatch I.T. provides managed services including security awareness programs
- Nexus IT Consultants delivers IT support with cybersecurity training options
- INTELITECHS serves businesses with security and compliance services
- 911 IT specializes in proactive security training designed for non-technical staff across nonprofit, healthcare, and professional services sectors
Large national providers often deliver standardized training modules through learning management systems with minimal customization. For a 15-person nonprofit, you're one account among thousands, and training content rarely addresses donor management systems or volunteer coordination platforms.
911 IT occupies the sweet spot - large enough to maintain 24-7 support infrastructure and stay current on evolving threats, small enough that every nonprofit client receives customized training addressing their specific workflows and compliance requirements. Founded in 2004, the company has built deep expertise in sectors where data protection is critical but IT budgets are constrained.
The flat-rate, transparent pricing model means nonprofits can budget accurately for ongoing training without surprise invoices when staff need extra support. The 100% satisfaction guarantee demonstrates confidence in training effectiveness.
Sam, who handles fundraising for a nonprofit, described the value: "By doing a security audit, I was able to not only find the security issues, I was also able to fix the issues, I sleep better knowing my systems and data are safe. The value of the information they provide is worth 10X what they are charging for the audit!"
For Salt Lake City nonprofits serious about protecting donor trust and mission continuity, security training isn't an IT checkbox - it's an investment in organizational resilience that pays dividends through prevented incidents and confident, security-aware teams.
Frequently Asked Questions
How long does initial security training take for nonprofit staff?
Initial comprehensive security awareness training typically requires 60-90 minutes covering phishing recognition, password management, data handling, and incident reporting. Training is broken into short modules that staff can complete at their own pace, with hands-on exercises reinforcing concepts. Follow-up quarterly refreshers take 15-20 minutes each, and monthly simulated phishing tests provide ongoing practice without disrupting daily nonprofit operations.
Can security training be customized for volunteer coordinators and fundraising staff?
Yes, effective security training includes role-specific tracks addressing distinct responsibilities. Volunteer coordinators receive modules on managing temporary access credentials and protecting beneficiary information. Fundraising staff get specialized training on donation platform security, donor database protection, and wire transfer verification. Executive directors learn about board reporting obligations and fiduciary responsibility for data protection under Utah regulations and grant compliance requirements.
What happens if a staff member fails a simulated phishing test?
Simulated phishing tests are learning opportunities, not punitive measures. Staff who click simulated phishing links receive immediate, non-judgmental coaching explaining what made the email suspicious and how to recognize similar threats. The goal is building skills and confidence, not creating fear. Organizations track improvement over time to measure program effectiveness and identify teams needing additional support through targeted refresher training.
How much does ongoing security awareness training cost for a small nonprofit?
Security awareness training is typically included as part of comprehensive cybersecurity services, which range from $25-$75 per user per month in the industry. This covers simulated phishing campaigns, quarterly refresher sessions, role-specific modules, and 24-7 helpdesk support for security questions. For nonprofits with limited budgets, this represents a cost-effective approach compared to recovering from a data breach that could cost tens of thousands in remediation and lost donor trust.
Do remote volunteers and part-time staff need the same security training?
Yes, anyone accessing donor databases, email systems, or beneficiary information needs security training regardless of employment status. Remote volunteers and part-time staff often face higher risk because they work from less-secure home networks and personal devices. Training delivery accommodates their schedules through self-paced online modules and flexible session timing. Special emphasis is placed on home network security, device protection, and secure file sharing for distributed teams.