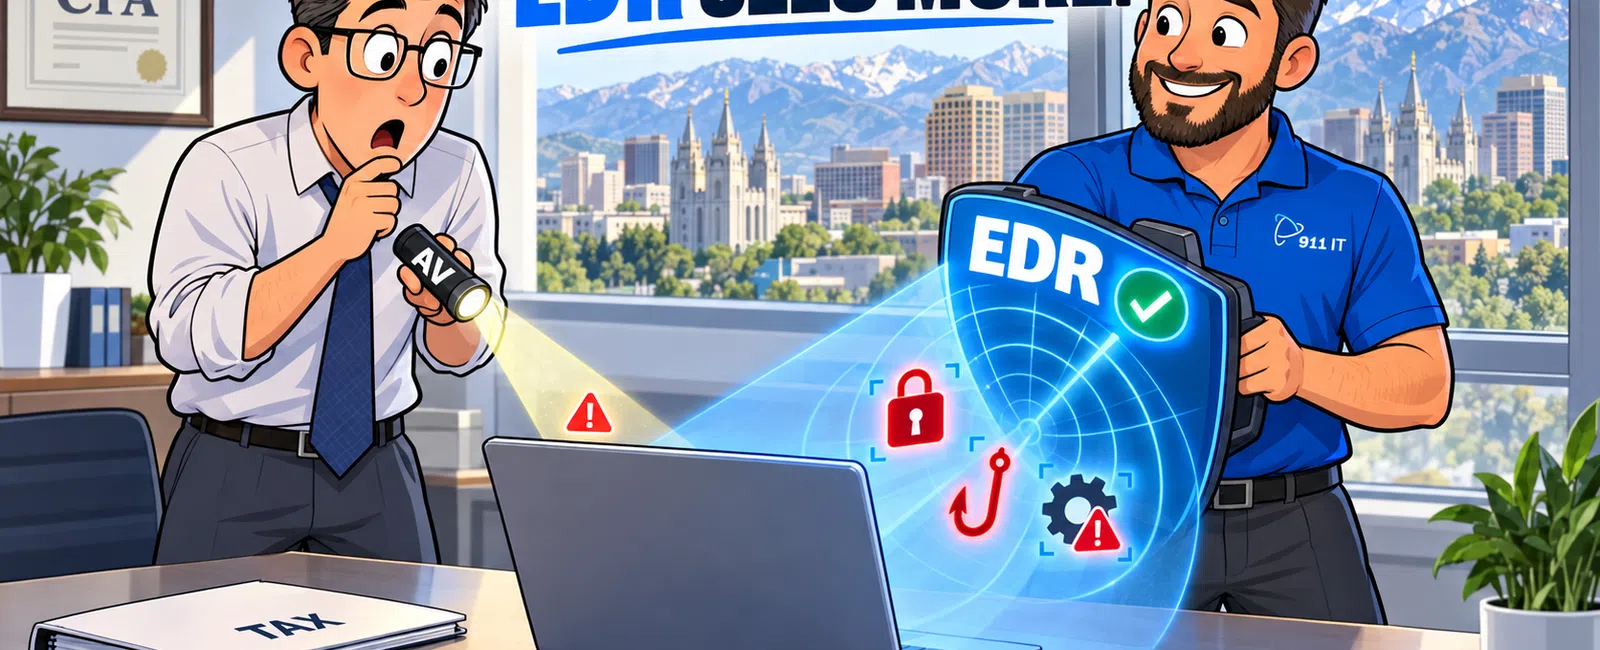
EDR (Endpoint Detection and Response) is significantly more advanced than traditional antivirus, offering real-time behavioral monitoring, threat hunting, and automated response capabilities that signature-based antivirus cannot match. While antivirus blocks known malware using signature databases, EDR monitors endpoint behavior continuously, detecting zero-day threats and sophisticated attacks that evade traditional defenses. For CPA firms handling sensitive client data, EDR reduces average breach detection time from 207 days to hours or minutes.
What Is the Core Difference Between EDR and Traditional Antivirus?
Traditional antivirus relies on signature-based detection, comparing files against a database of known malware signatures. When a file matches a known threat signature, the antivirus quarantines or deletes it. This approach works well for established threats but fails against new or modified malware.
EDR takes a fundamentally different approach by monitoring endpoint behavior in real time. Instead of just scanning files, EDR watches how programs interact with your system, looking for suspicious patterns like unauthorized access to client data, unusual network connections, or attempts to disable security tools.
The behavioral analysis capability means EDR can detect threats that have never been seen before. When ransomware attempts to encrypt your engagement files during tax season, EDR identifies the abnormal encryption activity and stops it, even if the ransomware variant is brand new.
EDR also provides visibility across your entire network. If one workstation shows signs of compromise, your IT team can investigate whether the threat has spread to other endpoints, trace the attack timeline, and understand exactly what data was accessed.
For Salt Lake City CPA firms subject to IRS data security requirements and Utah's breach notification laws, this visibility is critical for compliance reporting and incident response.
Does My CPA Firm Need Both EDR and Antivirus Protection?
Most modern EDR solutions include antivirus functionality as a foundational layer, making standalone antivirus redundant. EDR platforms incorporate signature-based detection alongside their advanced behavioral monitoring, giving you both protection methods in a single agent.
Running separate antivirus and EDR tools on the same endpoint can create conflicts. Both solutions compete for system resources, potentially slow down workstations during busy season, and may interfere with each other's detection mechanisms.
The practical answer for most accounting firms is that EDR replaces traditional antivirus entirely. You gain the signature-based protection you're familiar with, plus the advanced threat detection and response capabilities that modern threats demand.
However, EDR requires active management. Someone needs to monitor alerts, investigate suspicious activity, and respond to detected threats. A five-person CPA firm probably doesn't have dedicated security staff to watch EDR dashboards around the clock.
This is where managed detection and response (MDR) becomes valuable. An MDR provider monitors your EDR platform continuously, investigates alerts, and responds to threats on your behalf. Your team focuses on client work while security professionals handle threat hunting and incident response.
James, who runs a manufacturing company, shared his experience: "911 IT has been able to cut our IT expenditures by almost half and at the same time improve our systems reliability. Since moving to their IT Firm we have noticed that they are more knowledgeable than the other companies we have used in the past."
What Specific Threats Does EDR Catch That Antivirus Misses?
Ransomware variants evolve rapidly, with attackers releasing new versions specifically designed to evade signature-based detection. Traditional antivirus might recognize last month's ransomware strain but miss this week's variant that encrypts your client tax returns.
EDR detects ransomware by recognizing the encryption behavior itself, regardless of the specific malware variant. When a process suddenly starts encrypting hundreds of files, EDR flags this as suspicious and can automatically isolate the endpoint before your entire file server is encrypted.
Fileless malware operates entirely in memory without writing files to disk, making it invisible to traditional antivirus scans. These attacks use legitimate system tools like PowerShell to execute malicious commands. EDR monitors process behavior and command-line activity, detecting when legitimate tools are being abused for malicious purposes.
Credential theft attacks attempt to steal the passwords your staff use to access client portals, tax software, and bank reconciliation systems. EDR detects unusual authentication patterns, like a user account suddenly accessing systems it never touched before or attempting to log in from impossible geographic locations.
Lateral movement occurs when attackers compromise one workstation and then spread through your network to reach more valuable targets like your document management system or e-file credentials. EDR tracks network connections between endpoints and alerts when unusual communication patterns emerge.
EDR reduces the average time to detect a breach from 207 days to under 24 hours when properly monitored.
How Much Does EDR Cost Compared to Basic Antivirus?
Traditional antivirus typically costs between five and fifteen dollars per user per month for business-grade protection with centralized management. This covers signature-based scanning, scheduled scans, and basic quarantine capabilities.
EDR platforms with behavioral monitoring, threat hunting, and automated response capabilities typically fall in the $25 - $75 per user per month range as part of a comprehensive cybersecurity services package. This includes the EDR agent, the management platform, and varying levels of support depending on whether you manage it yourself or use an MDR service.
The price difference reflects the additional capabilities and infrastructure required. EDR platforms collect and analyze massive amounts of endpoint data, requiring cloud storage and processing power that basic antivirus doesn't need.
For a ten-person CPA firm, upgrading from basic antivirus to EDR might increase monthly security costs by $200 to $600. That investment needs to be weighed against the cost of a data breach involving client tax returns and financial records.
The average cost of a small business data breach now exceeds $150,000 when you account for forensic investigation, legal fees, client notification, regulatory fines, and lost business. For CPA firms, a breach during tax season can be catastrophic, potentially forcing you to turn away new clients when you can't guarantee data security.
Utah's breach notification law requires CPA firms to notify affected clients without unreasonable delay after discovering a breach. The notification process itself carries significant costs, and the reputational damage can last for years in a relationship-driven industry like accounting.
What Should Salt Lake City CPA Firms Look for in an EDR Solution?
Integration with your existing technology stack is critical. Your EDR solution needs to work seamlessly with your tax software, document management system, client portal, and remote desktop infrastructure without creating conflicts or performance issues.
Lightweight agents matter during tax season when every workstation is running resource-intensive applications. An EDR agent that consumes excessive CPU or memory will slow down tax preparation software and frustrate your team during your busiest months.
Automated response capabilities reduce the time between threat detection and containment. Look for EDR platforms that can automatically isolate infected endpoints, kill malicious processes, and prevent lateral movement without waiting for human intervention.
Forensic capabilities help you understand what happened during a security incident. When Utah's breach notification law requires you to report what data was accessed, you need detailed logs showing exactly which files were touched and when.
The management burden is often underestimated. EDR platforms generate alerts that require investigation and response. A five-person firm doesn't have staff to monitor security dashboards, so partnering with a provider offering managed detection and response becomes essential.
Local support matters when you need immediate help during a security incident. National EDR vendors route your calls through tier-one support queues where you're one ticket among thousands. A local managed IT services provider knows your firm, understands your tax season workflow, and prioritizes your emergency appropriately.
| Feature | Traditional Antivirus | EDR Solution |
|---|---|---|
| Detection Method | Signature-based scanning | Behavioral analysis + signatures |
| Zero-Day Protection | Limited to heuristics | Detects unknown threats by behavior |
| Threat Response | Quarantine/delete files | Isolate endpoints, kill processes, block network activity |
| Visibility | Individual endpoint only | Network-wide visibility and threat hunting |
| Forensics | Basic logs | Detailed timeline of attack progression |
| Ransomware Protection | Blocks known variants | Detects encryption behavior regardless of variant |
| Management Burden | Low (set and forget) | High (requires active monitoring) |
| Typical Cost | $5 - $15/user/month | $25 - $75/user/month |
How Do Salt Lake City CPA Firms Choose the Right Cybersecurity Partner?
CPA-specific experience matters significantly. An IT provider who understands engagement files, e-file security, and IRS Publication 4557 requirements will configure your security tools appropriately for your workflow rather than applying generic business security templates.
Tax season responsiveness is non-negotiable. When your EDR platform detects a threat on April 14th, you need immediate support, not a ticket queue where you're waiting behind dozens of other customers. The difference between a two-hour and a two-day response during busy season can determine whether you meet filing deadlines.
Several Salt Lake City providers serve CPA firms with varying approaches. Executech, Wasatch I.T., Nexus IT Consultants, INTELITECHS, ProLink IT, and Qual IT all offer managed IT services in the region. Each brings different strengths in terms of industry focus, service model, and scale.
Large national MSPs offer broad resources but treat small CPA firms as one account among thousands. Your support tickets enter queues managed by rotating junior technicians who don't know your firm or your tax season workflow. Escalation paths are slow, and you rarely speak with the same person twice.
Very small IT providers may offer personalized service but lack the depth to manage enterprise-grade security tools. When your EDR platform detects sophisticated threats, you need security specialists who understand threat hunting and incident response, not generalists who primarily handle password resets.
911 IT represents the sweet spot for CPA firms: large enough to deploy and manage advanced EDR platforms with continuous monitoring, small enough that every client is known by name and genuinely matters. The firm serves CPA and financial firms throughout Salt Lake City with proactive security monitoring and tax-season-aware support.
Garry, who runs an engineering firm with similar compliance needs, explained: "911 IT has been a local, personable partner that truly listens and works with us on detailed requests and advanced security compliance needs specific to our niche. We've had no major outages, and any minor issues were resolved quickly and effectively."
The firm's 100% Satisfaction Guarantee and flat-rate transparent pricing eliminate the uncertainty around security investments. You know exactly what you're paying each month, and if the service doesn't meet expectations, you're not locked into a contract that doesn't work.
With offices serving Salt Lake City, the broader Utah market, and expanding coverage in Wyoming and Arizona, 911 IT provides local responsiveness with the technical depth to handle sophisticated cybersecurity challenges. When your EDR platform alerts at 2 AM during tax season, you're calling a team that knows your firm and understands the urgency.
For CPA firms handling sensitive client data under IRS scrutiny and Utah regulatory requirements, EDR isn't optional anymore - it's the baseline for responsible data protection.
Frequently Asked Questions
Do I need antivirus if I have EDR?
Modern EDR solutions include signature-based antivirus functionality as a foundational layer, making standalone antivirus redundant. EDR provides both traditional malware scanning and advanced behavioral monitoring in a single platform. Running separate antivirus alongside EDR can create resource conflicts and performance issues. Most organizations replace traditional antivirus entirely when deploying EDR rather than running both simultaneously.
Is EDR the same as antivirus?
EDR and antivirus are fundamentally different technologies. Antivirus uses signature databases to identify known malware, while EDR monitors endpoint behavior in real time to detect threats by their actions rather than their signatures. EDR typically includes antivirus capabilities plus advanced features like threat hunting, automated response, and forensic investigation. Think of EDR as a comprehensive security platform that encompasses antivirus functionality plus significantly more.
Does EDR detect malware?
EDR detects both known and unknown malware through multiple methods. It includes signature-based detection for established threats and behavioral analysis for zero-day malware that has never been seen before. EDR monitors how programs interact with your system, flagging suspicious activities like unauthorized file encryption, credential theft attempts, or unusual network connections. This dual approach catches threats that traditional antivirus misses entirely.
Is EDR worth it for small CPA firms?
EDR is increasingly essential for CPA firms regardless of size due to IRS data security requirements and the sensitive nature of client financial data. While EDR costs more than basic antivirus, the average small business data breach now exceeds $150,000 in total costs. For firms handling tax returns and financial records, a breach during tax season can be catastrophic. EDR significantly reduces breach detection time and provides the forensic data required for regulatory compliance reporting.
How much does EDR cost per user?
EDR platforms typically cost between $25 and $75 per user per month as part of comprehensive cybersecurity services, compared to $5 to $15 per user monthly for basic antivirus. The price includes the EDR agent, management platform, and varying levels of monitoring support. Managed detection and response services, where security professionals monitor your EDR platform around the clock, fall at the higher end of this range but eliminate the burden of managing security alerts internally.
What happens if EDR detects a threat during tax season?
When EDR detects a threat, it can automatically isolate the affected endpoint, preventing the threat from spreading to other workstations or your file server. With managed EDR services, security professionals investigate the alert immediately and coordinate response with your team. The goal is containment within minutes rather than hours, minimizing disruption to tax preparation work. Detailed forensic logs document exactly what occurred, which is critical if client notification becomes necessary under breach disclosure laws.